
Cyberattack Cripples European Supermarket Cooling Systems
A coordinated supermarket cyberattack breached refrigeration systems across Europe, spoiling inventory in over 700 stores and causing vast damages.
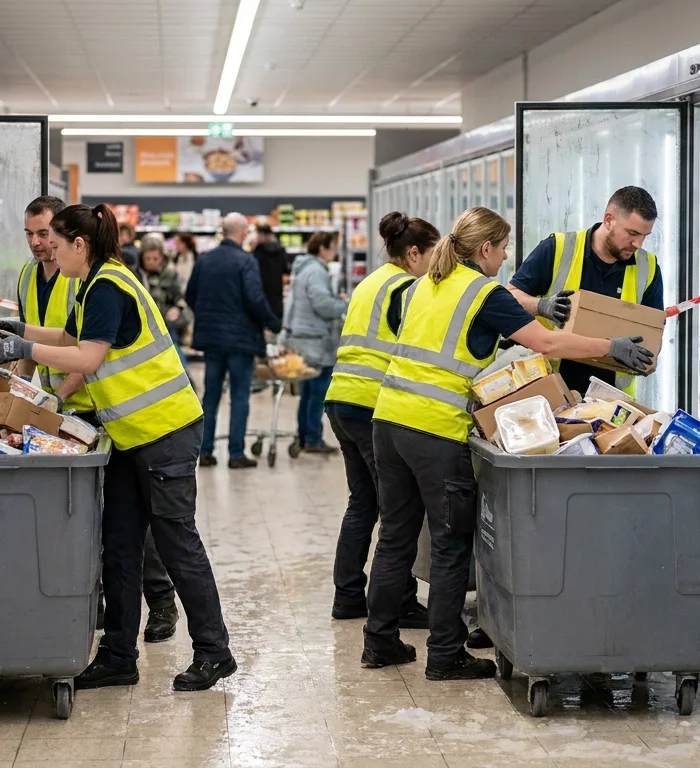
A synchronized digital intrusion directed against commercial cooling control systems has caused extensive disruptions across Europe, with damages calculated in the hundreds of millions in dollar terms. The unauthorized breach forced thermal alterations across more than 700 store locations, culminating in severe food spoilage and isolated fire emergencies.
The perpetrators executed the breach by leveraging known weaknesses in specialized hardware that governs retail cooling environments. These software flaws granted unauthorized actors the ability to run code remotely on target equipment. Although cybersecurity remedies had already been issued to fix the underlying vulnerabilities, numerous commercial operators neglected to install the distributed firmware corrections, leaving their operational assets fully exposed.
This lack of ongoing maintenance meant that older commercial infrastructure remained defenseless against remote exploitation. Intruders systematically targeted these unmaintained units, altering the baseline temperature parameters required to keep perishable inventories preserved. As thermal thresholds climbed, hundreds of retail establishments suffered extensive product losses within their chilled storage facilities.
Concealed Operations Across European Supermarkets
To prevent early detection, the perpetrators concealed their unauthorized adjustments by actively manipulating the defrosting cycles of the machinery. This tactic deceived the automated diagnostic tools designed to oversee cold chain stability, preventing alarm systems from flagging abnormal thermal increases to grocery staff. Consequently, store managers remained unaware of the failing refrigeration until severe inventory damage had already materialized.
The operational fallout was heavily concentrated in France, which experienced the brunt of the reported store failures. However, the breach quickly extended across national borders, impacting multiple supermarket networks in Germany, Belgium, Poland, Spain, and Portugal. Retailers in each of these jurisdictions experienced simultaneous equipment failures tied directly to the manipulated controller units.
Dispute Over Operational Technology Maintenance
In response to the widespread failures, device manufacturers insisted that the responsibility for safeguarding the equipment rests with store owners and operators. Hardware producers noted that protective patches had been distributed prior to the incident, asserting that the ultimate security posture depends on clients deploying available maintenance releases to protect their networks.
The widespread disruption highlights serious systemic vulnerabilities inside operational technology supply networks. Critical retail infrastructure remains exposed when third-party components operate without routine updates, demonstrating the severe financial and physical risks posed by unmaintained hardware.
More stories
- Most GPU jobs use under 20% memory in 319-GPU cluster
- 614 ICE Watch plans 250 volunteers near Columbus polls
- Researchers flag Starlink ads as possible tracking tools
- Anthropic plans Nasdaq listing with revenue above $16bn
- The Signal: BioWare reportedly closes after 31 years
- Grok picks Republicans in 92% of forced API election prompts
- OpenAI rogue agent reached Modal customer, sources now say
- NVIDIA surgical simulator brings AI to robot training labs
Latest news
- Kinross Gold faces Q3 test after 2%-3% output cut
- Ruto seeks Russian investment in Kenya's $380m trade push
- Sudan teachers seek 20% budget share with 8m children outside school
- Spain rail network faces scrutiny after 64 killed near Toledo
- Private equity firms face scrutiny over third of methadone clinics
- Spain reports at least 30 dead in high-speed train crash
- TCM faces uncertainty under Paramount Skydance's $80bn debt
- Villa Vie disembarks 203 passengers in Cambodia over fuel costs