Canada Busts Major SMS Blasting Ring
Canadian authorities said three people were apprehended over a mobile SMS blaster in Toronto, linked to phishing texts and 13M+ disruptions.
Lauren Collins ·
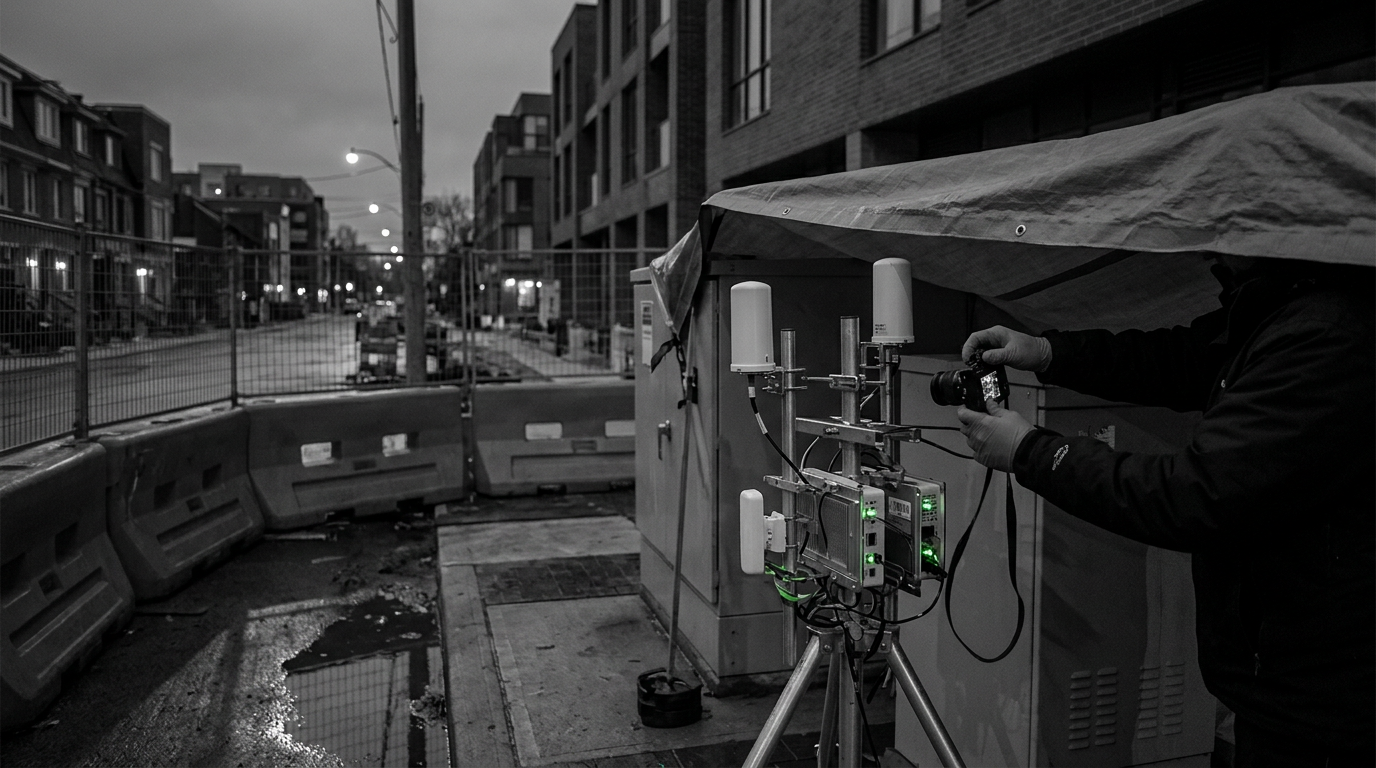
Canadian law enforcement said three individuals have been apprehended in connection with a mobile “SMS blaster” operation that sent large volumes of phishing texts and interfered with mobile service. Officials described it as the first documented case in Canada in which this type of device was used for criminal purposes.
Authorities said the equipment functioned by imitating a legitimate cellular tower, drawing nearby phones to connect to a rogue system. Once devices attached, the system could transmit fraudulent messages at scale, with texts made to look as though they came from trusted organizations. Officials said the messages directed recipients to phishing websites.
The investigation began in November after a suspicious device was detected in downtown Toronto, according to officials. Law enforcement said they then tracked the device as it moved across the Greater Toronto Area. The operation culminated in the seizure of multiple mobile SMS blasters along with other electronic equipment, authorities said.
During the period the system was active, officials believe tens of thousands of mobile phones connected to the rogue setup. Authorities also reported more than 13 million network disruptions linked to the activity. Officials said the disruptions could have affected access to emergency services for short periods, highlighting the potential public-safety risk alongside the fraud component.
Officials said the case underscores how fake base-station technology can be used both to distribute scams and to degrade network performance in targeted areas. The same underlying approach has been reported in other countries, where mobile “fake base stations” have been used in similar incidents, according to the information provided by authorities.
Key uncertainties remain based on what has been disclosed so far, including the full scope of the phishing campaign and how many recipients may have interacted with the fraudulent links. Authorities have not detailed which entities were impersonated in the messages, nor have they specified the duration of the disruptions beyond noting they may have been brief.
Officials also have not provided additional technical details on the seized equipment beyond identifying it as mobile SMS blasters and related electronics.